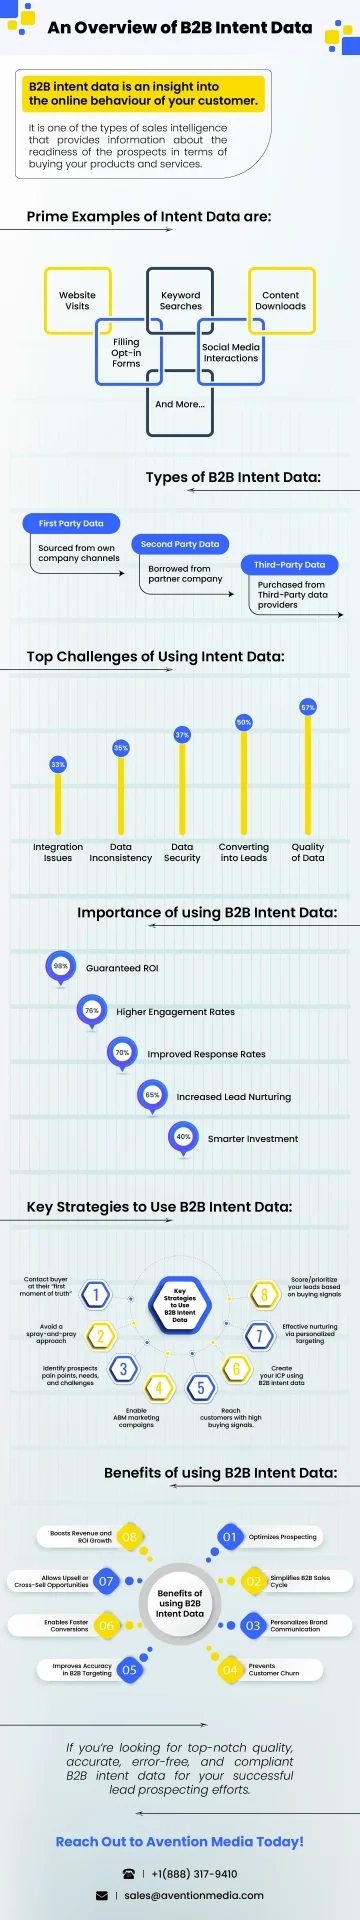
What Is Technographic Data
Understand what technographic data is, how it is collected, and how top B2B revenue teams use software stack intelligence to accelerate outbound sales.
Connect your SIEM implementation offer with the organizations and professionals it serves. Request a Microsoft Sentinel users email list covering SOC directors, Sentinel administrators and company details for targeted financial services campaigns.
Review the format for a Microsoft Sentinel campaign before requesting contact records.
| Contact Name | Technology Role / Function | Technology Category / Product | Company Name | Company ID | Email Address | Direct Phone | Company Size | City | State | Country | LinkedIn Profile |
|---|---|---|---|---|---|---|---|---|---|---|---|
| Quinn Turner | SOC Director | SIEM modernization | Cloud-native SIEM and security analytics | Northstar Systems | ORG-****0700 |
q.tu****@sample-700.example |
+1 (200) 555-**** |
500-999 employees | Austin | TX | United States | linkedin.com/in/quinn-turn-**** |
| Parker Cox | SIEM Architect | detection engineering | Cloud-native SIEM and security analytics | Cedarline Group | ORG-****0701 |
p.co****@sample-701.example |
+1 (201) 555-**** |
1,000-4,999 employees | Atlanta | GA | United States | linkedin.com/in/parker-cox-**** |
| Rowan Kelly | Security Operations Manager | security data integration | Cloud-native SIEM and security analytics | BluePeak Solutions | ORG-****0702 |
r.ke****@sample-702.example |
+1 (202) 555-**** |
5,000-9,999 employees | Boston | MA | United States | linkedin.com/in/rowan-kell-**** |
| Blake Murphy | Threat Detection Lead | SIEM modernization | Cloud-native SIEM and security analytics | Summit Services | ORG-****0703 |
b.mu****@sample-703.example |
+1 (203) 555-**** |
10,000+ employees | Raleigh | NC | United States | linkedin.com/in/blake-murp-**** |
| Finley Reed | CISO | detection engineering | Cloud-native SIEM and security analytics | Redwood Partners | ORG-****0704 |
f.re****@sample-704.example |
+1 (204) 555-**** |
100-499 employees | Phoenix | AZ | United States | linkedin.com/in/finley-ree-**** |
Verified installed base contact records across 190+ countries and regions.
Choose the information needed to qualify Microsoft Sentinel accounts with verified contact intelligence, firmographics, and technology attributes.
Verified IT leaders, decision-makers, business emails & direct dials
Enterprise firmographics, headquarters, employee tiers & revenue
Microsoft Sentinel, connected ecosystem & hybrid stacks
Global industry sectors, 4-digit SIC codes & 6-digit NAICS codes
IT hiring velocity, cloud migration intent & active buying triggers
| Name | Daniel R. |
| Business Email | d•••••@northwind.com |
| Direct-Dial | +1 (415) •••-••42 |
| Job Title | VP, Infrastructure |
| Seniority | VP |
| Department | IT Operations |
| Location | Austin, TX |
| Confidence Score | 96% |
Illustrative sample with masked values. Actual fields and formats vary by order.
Choose the responsibilities relevant to your offer. A SIEM implementation campaign may need different stakeholders from a SOC automation campaign within the same Microsoft Sentinel account.
For SIEM implementation, request SOC directors whose work intersects with Microsoft Sentinel.
Target Sentinel administrators for discussions about log source integration. Ask for the corresponding department and seniority fields to distinguish a Microsoft Sentinel operational contact from an executive sponsor.
Reach detection engineering leads at qualified Microsoft Sentinel organizations when presenting detection engineering.
Include security architecture managers when your Microsoft Sentinel offer concerns SOC automation. Pair the title with the person's actual remit in security analytics operations so your message reaches the owner of the relevant decision.
Microsoft Sentinel is the security analytics service previously known as Azure Sentinel. Distinguish it from Defender endpoint products and general Azure adoption.
Use Sentinel service as an explicit selection criterion. Add connected security tools where the evidence supports it and where it affects your SIEM implementation offer.
Define whether you need SOC directors, Sentinel administrators or another relevant owner. Match the contact to detection engineering rather than selecting solely by seniority.
Specify employee and revenue ranges suitable for log source integration. Keep company size separate from software seats, managed devices or technical instances in a Microsoft Sentinel environment.
Prioritize financial services when that is your market. Add adjacent industries only when your Microsoft Sentinel service and delivery experience fit their requirements.
Request Microsoft Sentinel records by US state, city or territory.
Choose the business emails, phone fields and company attributes needed for your Microsoft Sentinel campaign.
The supplied research model gives a planning view of the Microsoft Sentinel market.
Modeled organizations associated with the defined Microsoft Sentinel scope
Modeled business and technical profiles relevant to security analytics operations
Modeled profiles associated with US organizations
Use these breakdowns to assess audience coverage by job seniority, location, company size, industry, and revenue.
The following applications connect security analytics operations with concrete services.
Build a Microsoft Sentinel segment for providers of SIEM implementation.
Use Microsoft Sentinel account context to introduce log source integration to Sentinel administrators.
For detection engineering, prioritize relevant Microsoft Sentinel professionals such as detection engineering leads. Ask for connected security tools where supported and use the result to qualify the technical conversation.
Approach security architecture managers with a defined SOC automation proposal for Microsoft Sentinel environments. Qualify Sentinel service before outlining deliverables so your team can explain why the account fits the offer.
Build a Microsoft Sentinel segment for providers of managed security operations.
Use Microsoft Sentinel account context to introduce SIEM migration to Sentinel administrators.
For security reporting, prioritize relevant Microsoft Sentinel professionals such as detection engineering leads. Ask for Sentinel service where supported and use the result to qualify the technical conversation.
Approach security architecture managers with a defined analyst training proposal for Microsoft Sentinel environments.
A Microsoft Sentinel customers list should reduce the research between identifying an account and choosing a relevant professional.
Require Sentinel service
Technology qualification may need additional research
Select Sentinel administrators or the functional owner of log source integration
Broad job titles may not identify the application owner
Add connected security tools when the offer requires it
Company information may not describe the relevant workflow
Review Microsoft Sentinel evidence and contact fields together
Contact completeness alone does not prove product relevance
Combine Microsoft Sentinel use with industry, company size and US location
Geography by itself may produce out-of-scope accounts
If your Microsoft Sentinel campaign for log source integration spans adjacent environments, review related technology lists.
For Microsoft Sentinel, a useful starting point combines Sentinel service with the roles responsible for SIEM implementation.
| Selection Parameter | Details & Targeting Guidance |
|---|---|
| Technology | Microsoft Sentinel, Sentinel service and any additional product evidence required |
| Professionals | SOC directors, Sentinel administrators and other owners of security analytics operations |
| Company profile | Financial services, preferred employee range and revenue range |
| Location | USA, named states or additional international markets, with location Basis specified |
| Fields and exclusions | Business contact channels, connected security tools where available, customer domains and suppression criteria |
Evaluate your Microsoft Sentinel sample on two dimensions: product relevance and contact usability. Confirm that records match Sentinel service, then inspect the business email and role information needed for SIEM implementation.
A strategic blueprint illustrating multi-channel outreach routing and qualification.
An SOC consultancy targeting US financial firms needs detection engineering and Sentinel platform owners who oversee log onboarding and alert handling.
The request can specify financial services accounts, Sentinel service, connected security tools where available, and relevant Sentinel administrators.
Route operational questions to Sentinel administrators and broader planning discussions to SOC directors.
Answers to common questions regarding database accuracy, compliance, verification timing, and targeting parameters.
It is a business contact dataset organized around companies associated with Microsoft Sentinel. It can combine relevant SOC directors, Sentinel administrators and company information for campaigns related to security analytics operations.
Provide the Sentinel service needed for your offer, then specify company size, industry and territory.
For Microsoft Sentinel targeting, request names, business emails, job titles, company websites, industry and location. Add connected security tools where available when that information affects compatibility with log source integration.
Yes. Define the US territories and relevant Microsoft Sentinel responsibilities such as SOC directors and detection engineering leads.
No. Treat Azure Sentinel as a historical search alias and reconcile the same product environment.
Providers of SIEM implementation, detection engineering and managed security operations can use the dataset to identify relevant accounts and professionals. The request should name the business problem and the responsible team in security analytics operations.
Request validation details for the Microsoft Sentinel contacts you intend to order.
No. Microsoft Sentinel adoption indicates potential relevance to log source integration or related services.
The Microsoft Sentinel working model contains 17,500 companies, 36,900 global profiles and 16,600 USA profiles. These are research estimates. Actual availability depends on Sentinel service, role selection and your target locations.
Confirm how exclusions will be applied before the final Microsoft Sentinel company and contact totals are prepared.
Tell us which Microsoft Sentinel environments and SOC directors belong in your campaign. Review the available fields and request a count aligned with log source integration.
Understand what technographic data is, how it is collected, and how top B2B revenue teams use software stack intelligence to accelerate outbound sales.